

Threat Index
Plataforma: Hack The Box
Dificultad: Very Easy
Categoría: Coding
🔗 Link del challenge: https://app.hackthebox.com/challenges/Threat%20Index
Descripción
You are monitoring data streams exiting suspicious TOR nodes, believed to be part of the Empire of Volnaya’s covert APT infrastructure. As Talion “Little Byte” Reyes you’ve been assigned to identify and evaluate indicators of compromise embedded in the exfiltrated traffic.
Dado un stream de datos (letras minúsculas y dígitos), debemos calcular su threat score usando la fórmula:
threat score = Σ (ocurrencias del keyword × peso del keyword)Los keywords y sus pesos son:
| Keyword | Peso |
|---|---|
| scan | 1 |
| response | 2 |
| control | 3 |
| callback | 4 |
| implant | 5 |
| zombie | 6 |
| trigger | 7 |
| infected | 8 |
| compromise | 9 |
| inject | 10 |
| execute | 11 |
| deploy | 12 |
| malware | 13 |
| exploit | 14 |
| payload | 15 |
| backdoor | 16 |
| zeroday | 17 |
| botnet | 18 |
Ejemplo:
Input:  payloadrandompayloadhtbzerodayrandombytesmalware
Output: 60payload× 2 → 30zeroday× 1 → 17malware× 1 → 13- Total = 60
Solución
Usamos str.count() para contar las ocurrencias de cada keyword en el stream y acumulamos el score en una sola línea:
keywords = {
    "scan": 1, "response": 2, "control": 3, "callback": 4,
    "implant": 5, "zombie": 6, "trigger": 7, "infected": 8,
    "compromise": 9, "inject": 10, "execute": 11, "deploy": 12,
    "malware": 13, "exploit": 14, "payload": 15, "backdoor": 16,
    "zeroday": 17, "botnet": 18
}

stream = input()
print(sum(stream.count(kw) * w for kw, w in keywords.items()))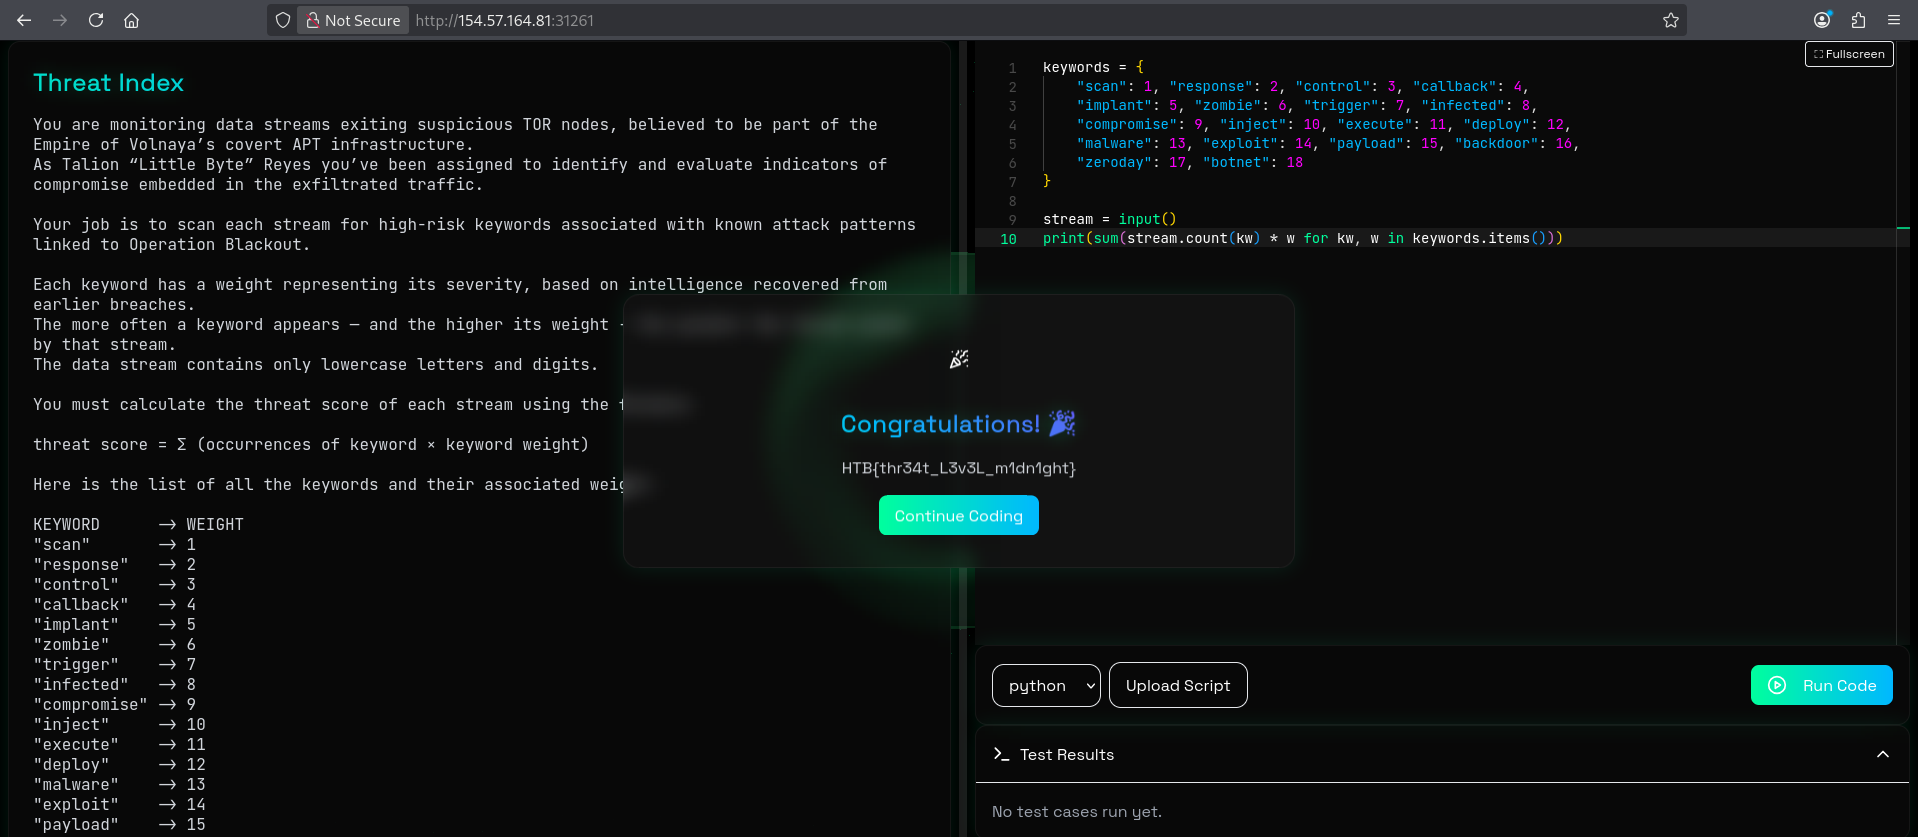
Flag
HTB{thr34t_L3v3L_m1dn1ght}Challenge Threat Index de Hack The Box completado.